Approach
A method you can audit.
Security testing asks for trust. We earn it with a method that is written down, agreed in advance and visible at every step.
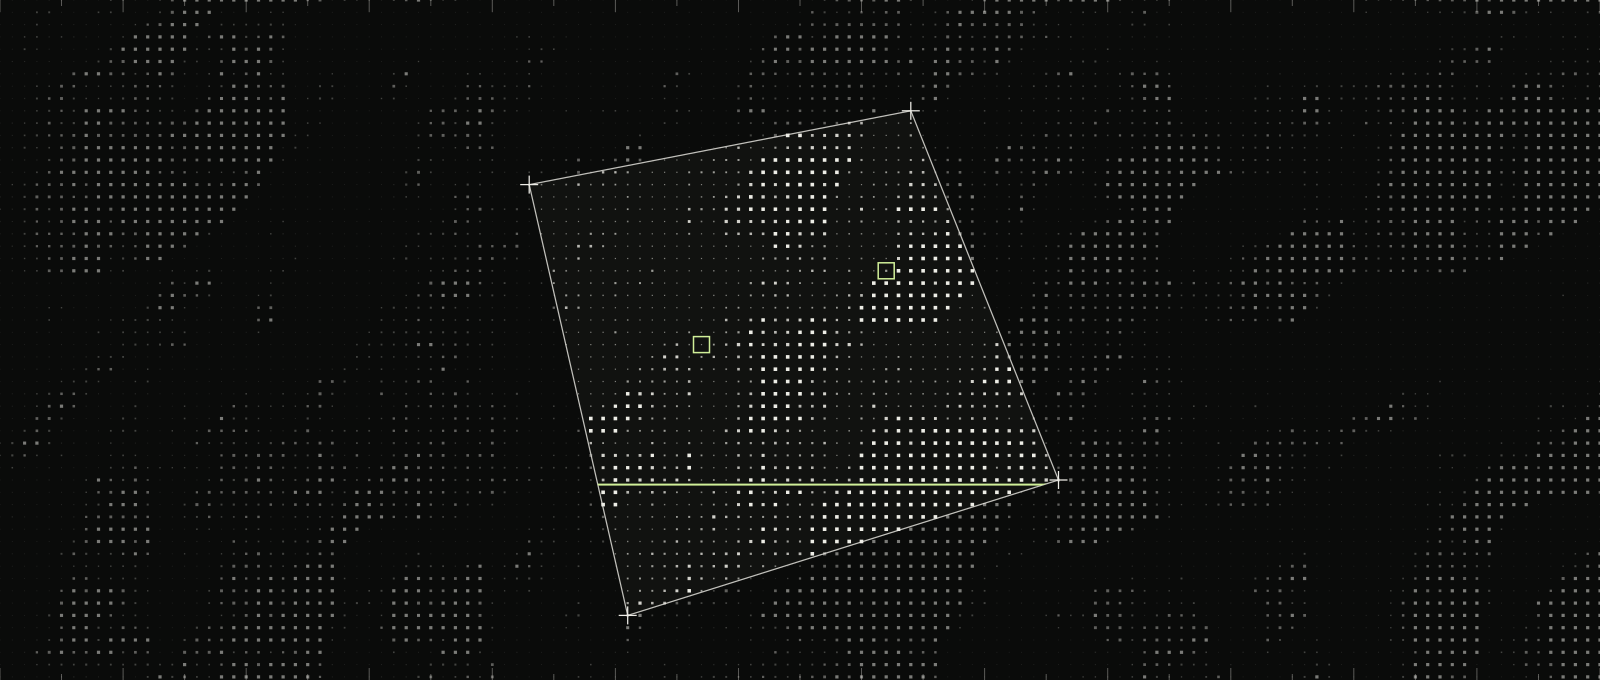
Fig. 01 — Scope boundary
Testing happens inside the authorized boundary. Nothing happens outside it.
- Authorized scope
- Test front
- Evidence
Six phases
From permission to proof.
Map
We model the in-scope system, its components, entry points, identities, data flows and trust boundaries, and agree with you where testing effort should concentrate.
- You provide
- Documentation or access you choose to share
- What would concern you most
- You receive
- A test plan aligned to your priorities
Test
AI agents run broad, repeatable exploration inside the agreed scope. Our testers direct the work, pursue promising leads and attempt to confirm real impact within the rules of engagement. Critical issues are reported promptly.
- You provide
- Availability of the agreed contacts
- You receive
- Prompt notice of critical issues, as set out in the rules of engagement
Evidence
Each finding records what was tested, what happened, the evidence captured and how confident we are. Confirmed issues stay separate from hypotheses, and a person reviews every finding before it reaches you.
- You receive
- A findings report with supporting evidence
Remediate
We explain the root cause of each finding and practical ways to fix it in the context of your system, prioritized by impact and effort, then take your team through them in a debrief.
- You provide
- Time with the engineers who own the fixes
- You receive
- Remediation guidance
- A debrief with your team
Retest
When retesting is in scope, we test the fixes and record what changed, and what did not.
- You provide
- Notice when fixes are ready
- You receive
- A retest note
Where AI fits
Agents cover the ground. Testers make the call.
AI agents let a small team cover more of the agreed scope, more consistently. They work only inside that scope, directed by our testers, and a person reviews every finding before it reaches you.
Exploring the scope
- AI agents
- Broad, repeatable exploration
- NOSYSTEM testers
- Set direction and priorities
Spotting candidate issues
- AI agents
- Surface anomalies and signals
- NOSYSTEM testers
- Decide what merits investigation
Confirming impact
- AI agents
- Support with controlled checks
- NOSYSTEM testers
- Verify within the rules of engagement
Reporting
- AI agents
- Assemble the record of what was tried
- NOSYSTEM testers
- Write, review and stand behind findings
Boundaries
Lines we do not cross.
- No testing without written authorization.
- Nothing outside the agreed scope, windows or rules of engagement.
- High-risk techniques only with explicit, prior agreement.
- No finding reported without evidence and human review.
- No claim that a system is secure. We report what was tested, what was found and what was not covered.